Skip to content
No results
  • Home
  • About Us
  • Blog
  • Bootcamp
  • Contact Us
Secure Coding Practices
  • Home
  • About Us
  • Blog
  • Bootcamp
  • Contact Us
Secure Coding Practices
  • Input Validation & Sanitization

Mastering Parameterized Queries for DB Security
Mastering Parameterized Queries for DB Security

Implementing Parameterized Queries for DB Security is essential for development teams aiming to block SQL injection vulnerabilities and protect modern database architectures. At Secure Coding Practices, security architects emphasize that separating user data from execution logic prevents malicious payloads from…
  • Leon I. Hicks
  • October 15, 2026
  • impact improper canonicalization handling, Understanding Input Canonicalization

Impact of Improper Canonicalization Handling

Canonicalization flaws can cause security checks to approve one form of input while another component interprets it as a different resource, route, or command. MITRE CWE-180 describes this as a validation-order problem: the application checks data before it has been…

  • Leon I. Hicks
  • October 14, 2026
  • Input Validation & Sanitization, Libraries handling canonicalization securely, Understanding Input Canonicalization

How Libraries Handle Canonicalization Securely

Data flow diagram showing libraries handling canonicalization securely before granting file access.

Canonicalization should turn equivalent input into one clear form before authorization, but it can’t replace the final security check. The application still needs to enforce access rules when it performs the requested resource operation. Path handling is a common source…

  • Leon I. Hicks
  • October 13, 2026
  • Testing for canonicalization vulnerabilities methods, Input Validation & Sanitization, Understanding Input Canonicalization

Testing for Canonicalization Vulnerabilities: Methods

testing for canonicalization vulnerabilities methods with input equivalence and validation checks.

Canonicalization testing checks whether each layer reads the same input in the same way. That matters because security checks can fail when one layer decodes, normalizes, or rewrites data before another layer uses it. MITRE CWE-180 points to validation before…

  • Leon I. Hicks
  • October 12, 2026
  • validating input after canonicalization important, Input Validation & Sanitization, Understanding Input Canonicalization

Validating Input After Canonicalization Matters

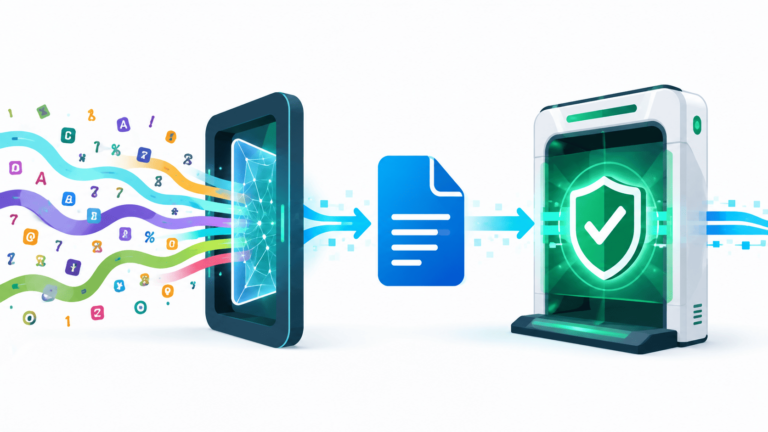
Phone data streaming into a document then a secure server, showing why validating input after canonicalization important.

Validate input after canonicalization, not before. Security checks should inspect the same form of data the application will use. MITRE lists this ordering issue as CWE-180, which covers validation before canonicalization and can contribute to problems such as path traversal.…

  • Leon I. Hicks
  • October 11, 2026
  • Understanding Input Canonicalization, Input Validation & Sanitization, normalizing user input securely best practices

Normalizing User Input Securely: Best Practices

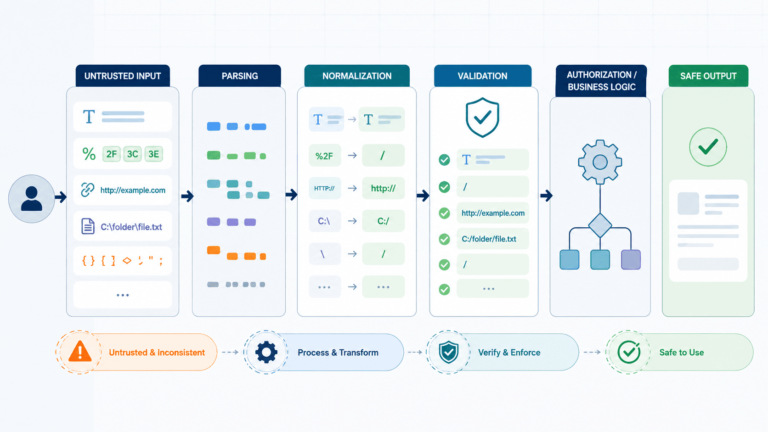
Diagram illustrating normalizing user input securely best practices from untrusted input to safe output.

Secure Coding Practices explains why secure input normalization should happen before validation and security checks. Untrusted data needs a consistent internal form first. If validation runs too early, later decoding or canonicalization may reveal content that bypassed those checks. So…

  • Leon I. Hicks
  • October 10, 2026
  • Understanding Input Canonicalization

UTF 8 Encoding Attacks Canonicalization: A Simple Guide 

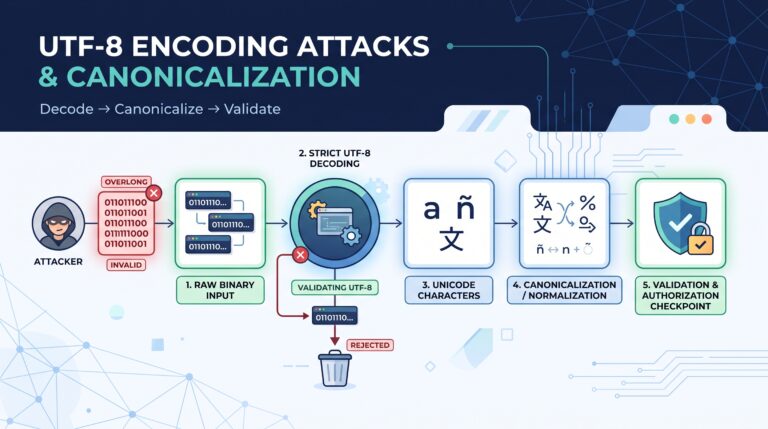
Secure processing steps designed to mitigate UTF-8 encoding attacks canonicalization threats.

UTF 8 encoding attacks canonicalization can cause security gaps when one layer checks input differently from the component that later decodes or normalizes it. Invalid UTF-8, overlong sequences, and repeated decoding can make safe-looking input change meaning after validation. RFC…

  • Leon I. Hicks
  • October 9, 2026
  • Understanding Input Canonicalization

Double Encoding Attack Explained Simply: How It Works? 

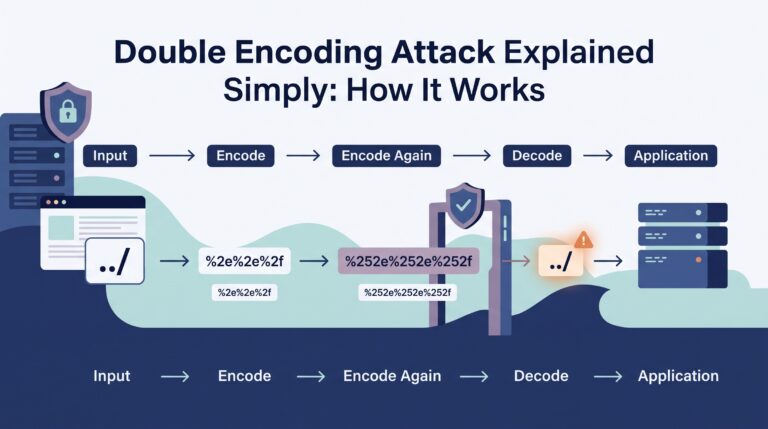
System layout demonstrating request traversal and security filter bypass in a double encoding attack explained simply.

A double encoding attack explained simply is an attack that encodes input twice to hide its real meaning from security checks. A filter may decode the value once and see harmless encoded text, while the application decodes it again and…

  • Leon I. Hicks
  • October 8, 2026
  • Understanding Input Canonicalization

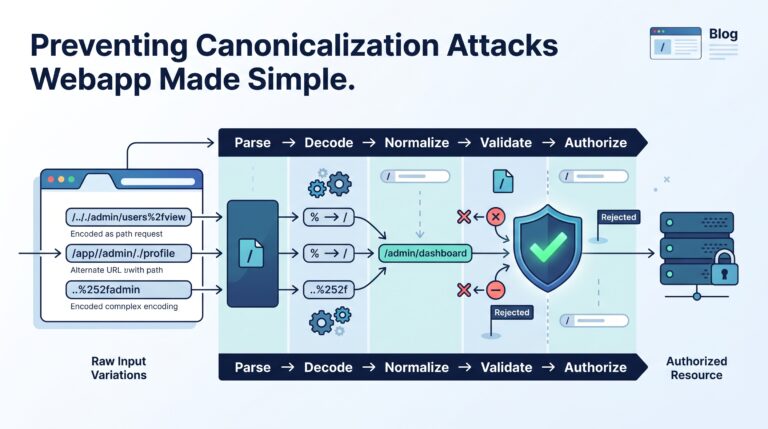
Preventing Canonicalization Attacks Webapp Made Simple 

Process flow illustration for preventing canonicalization attacks webapp by merging path variations into one form.

Preventing canonicalization attacks webapp starts with converting security-sensitive input into one trusted representation before validation and authorization. This helps stop attackers from exploiting different interpretations of paths, URLs, encoded values, or identifiers across application layers.  Secure Coding Practices recommends treating…

  • Leon I. Hicks
  • October 7, 2026
  • Understanding Input Canonicalization

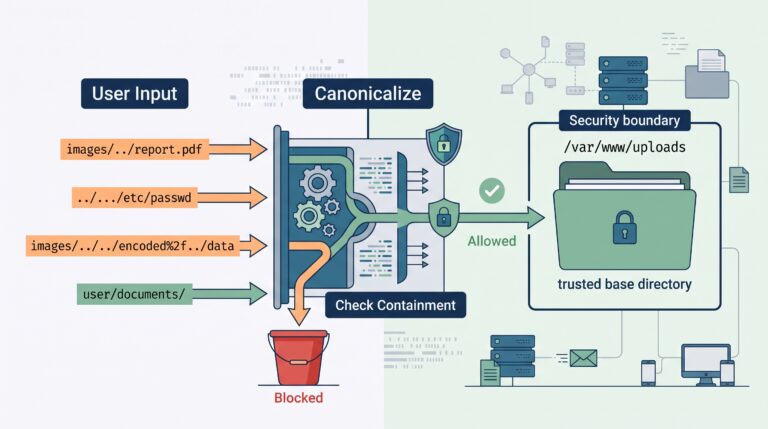
Path Traversal Canonicalization Example: Avoid Common Bypasses 

Visualization of input processing using a path traversal canonicalization example to separate allowed and blocked paths.

Path traversal canonicalization example shows how resolving a user-controlled path before validation can prevent unauthorized file access. CWE-22 covers improper limitation of a pathname to a restricted directory, which can let attackers reach files outside an approved location. In practice,…

  • Leon I. Hicks
  • October 6, 2026
1 2 3 4 … 57
Next
Secure Coding Practices

Join a thriving global community of developers dedicated to writing cleaner, safer, and more resilient code. Whether you're just starting out or leveling up your skills, this bootcamp gives you the practical knowledge and hands-on experience needed to identify vulnerabilities, apply secure coding principles, and build software that stands up to real-world threats.

Join the Next Bootcamp →

  • About us
  • Blog
  • Bootcamp
  • Disclaimer
  • Contact us
  • Privacy Policy
  • Terms & Conditions

Copyright © 2026 SecureCodingPractices.com — All rights reserved.