

Securing modern web architectures requires a shift in how developers handle object transport. As applications become increasingly distributed, the reliance on serialized data formats has introduced critical security gaps.
At Secure Coding Practices, we focus on identifying and neutralizing these high-risk flaws before they compromise your production environment. Implementing robust defensive measures, specifically using integrity checks deserialization, acts as a primary barrier against unauthorized object instantiation and malicious payload execution.
Core Deserialization Security Principles
Securing modern applications requires a comprehensive understanding of how object states are handled across different architecture layers.
- Insecure deserialization occurs when untrusted data is processed without sufficient validation, potentially allowing for malicious object instantiation.
- Proactive identification of gadget chains within third-party dependencies is essential for accurate risk assessment.
- Effective testing must move beyond basic input validation to analyze the entire application logic flow.
Why Is Using Integrity Checks Deserialization Essential for Data Security?
The primary reason to prioritize this defense is the catastrophic nature of the vulnerability. When an application reconstructs an object from an untrusted byte stream, it often implicitly trusts the data, failing to verify the class type or content.
If your infrastructure lacks rigorous checks, you are at risk of data tampering that frequently bypasses traditional firewalls. By implementing cryptographic verification, you gain visibility into how your application handles incoming serialized input.
This ensures that only authorized, untampered classes are instantiated within the application memory. Without specific verification layers, these flaws often remain hidden in the deep logic of your codebase, inaccessible to standard scanners that look only for common web vulnerabilities. Using integrity checks deserialization transforms your data handling from a passive process into an active, verified security control.
How Do Application Vulnerabilities Relate to Data Integrity?
To test effectively, you must understand the transition of data from storage to execution. Serialization transforms complex objects into a stream of bytes for efficient transmission or storage. Deserialization is the reverse, restoring that stream into an active object within your application memory.
The vulnerability emerges when the application does not constrain the reconstruction process. An attacker can manipulate the byte stream to force the application to instantiate unintended classes. Once these malicious objects are in memory, they can trigger gadget chains, which are sequences of existing code within your application that perform unauthorized actions.
Because these risks are pervasive across modern tech stacks, it is vital to understand the dangers of insecure deserialization to better secure your data endpoints.
- Data Stream: The input provided to the application, often containing serialized objects.
- Gadget Chain: A series of methods already present in the application code or libraries, which can be linked to perform an exploit.
- Sink: The specific code location where the untrusted data is processed.
What Are Common Examples of Deserialization Exploits in Java Environments?
When you begin the process of auditing your codebase, you must move beyond superficial checks. A systematic methodology ensures that you do not miss complex gadget chains. If you are aiming for long-term security, you should analyze how different languages handle serialization logic.
The exploitation process often relies on the specific language’s ability to instantiate objects dynamically. For instance, developers frequently study insecure deserialization attack examples in Java to understand how attackers leverage standard library classes to achieve remote code execution.
A structured plan for securing your serialization modules prevents critical oversights and ensures comprehensive coverage across all application modules. If you are currently managing these modules in a CI/CD pipeline, ensure that your automated tests are configured to detect gadget chains early.
Passive reconnaissance involves mapping out all areas where serialization is utilized. Look for base64 encoded strings, binary objects in cookies, or hidden form fields that suggest serialized data is being passed back and forth. Gadget discovery requires analyzing the libraries in use, focusing on third-party dependencies rather than just your own code.
How Do You Set Up a Safe Environment for Deserialization Testing?
You should never perform active testing against production systems. Deserialization attacks can cause severe instability, including service crashes that disrupt legitimate users. A proper lab environment is the cornerstone of your security audit.
- Isolate the Environment: Utilize a sandbox or a containerized environment that mirrors your production configuration but lacks connectivity to your live database or sensitive user data.
- Instrument the Application: Use debuggers and remote logging to capture the internal state of the application during the deserialization process. This allows you to observe what classes are being instantiated.
- Document Baseline Behavior: Before introducing payloads, ensure you have a baseline of how the application processes valid objects. This makes it easier to identify anomalies during your active testing phases.
Testing in a controlled environment allows you to push boundaries without the fear of damaging critical infrastructure. It also provides the space to experiment with different gadget chain combinations that might be too unstable for a live system.
What Are the Best Practices for Preventing Insecure Deserialization in .NET and PHP?
Platform-specific vulnerabilities require tailored defense mechanisms. For developers working within these ecosystems, we recommend reviewing our comprehensive guide on preventing insecure deserialization in .NET and PHP to implement robust security controls.
These languages often handle object reconstruction in ways that can be exploited if developers are not careful with object serialization libraries. Implementing strict class whitelisting is a universal requirement across both .NET and PHP architectures to ensure that the deserializer only accepts trusted types.
Additionally, teams must prioritize updating their dependencies to avoid known gadget chains. Vulnerable libraries act as the primary vector for attackers to gain arbitrary code execution, regardless of how secure the developer’s custom code appears to be.
How Can You Detect Complex Gadget Chains During Analysis?
Detecting gadget chains requires a blend of static analysis and dynamic observation. You must look beyond your own code to understand the third-party libraries that compose your application stack.
“Deserialization of untrusted data can lead to arbitrary code execution, denial of service, or other malicious actions.” – CWE-502 Documentation
Many developers assume that using a standard, popular library ensures safety, but these libraries often contain complex gadget chains that attackers have already mapped out. To identify these chains, follow these systematic analysis steps:
- Perform Static Code Analysis: Use automated tools to scan your codebase for dangerous sinks where untrusted data is deserialized. This identifies where you might be exposed.
- Map Classpath Dependencies: Document every library used in your application. Check these against databases that track known gadget chains to see if your dependencies are vulnerable.
- Trace Data Sinks: Follow the flow of user-controlled data into your application. If a byte stream reaches a deserialization sink without prior validation, flag it for immediate review.
- Observe Runtime Behavior: In a sandbox environment, use debuggers to watch how objects are instantiated.
By mapping these chains, you gain the visibility required to remediate risks before they are exploited in the wild.
Why Is the Remote Code Execution Deserialization Impact So Severe?
The primary danger of deserialization lies in the capability for an attacker to gain full server control. When an attacker successfully triggers a gadget chain, they can execute arbitrary commands with the same privileges as the application process.
This allows them to perform several malicious actions:
- Exfiltrate Sensitive Data: Gain direct access to your database or configuration files, potentially leaking customer information or proprietary code.
- Establish Persistence: Install backdoors that ensure the attacker maintains access even after the application restarts or the initial vulnerability is patched.
- Lateral Movement: Use the compromised application as a pivot point to attack other internal systems that are not directly exposed to the internet.
- Deploy Malware: Run unauthorized processes, such as cryptominers or ransomware, directly on your production infrastructure.
The severity stems from the fact that the application itself executes the malicious payload. Because the server trusts the code that it is running, traditional security controls often fail to detect the attack, making this a high-priority threat for any organization that processes serialized data.
How Should You Report Your Testing Findings?
Reporting your results after testing requires more than just identifying the presence of a flaw. Because these vulnerabilities are complex, your report must clearly articulate the risk to stakeholders.
A high-quality report helps security teams prioritize remediation and justifies the necessary engineering resources. When documenting your findings, ensure you include:
- Proof of Concept (PoC): Provide a clear, reproducible exploit payload that demonstrates the vulnerability without causing irreversible damage.
- Impact Assessment: Detail exactly what an attacker could achieve. For instance, describe how the flaw leads to unauthorized file access, remote code execution, or data manipulation.
- Gadget Chain Trace: Document the path from the sink to the final execution of the malicious command. This helps developers understand which specific libraries or methods are responsible.
- Business Context: Explain how this vulnerability affects specific business assets. Does it expose customer records, credentials, or sensitive proprietary algorithms?
- Remediation Roadmap: Suggest specific, actionable steps for the development team to mitigate the issue.
How Can You Remediate Deserialization Vulnerabilities?
Remediation is not just about patching the code; it is about changing how your application handles data. Once you have identified a vulnerability, you must prioritize moving your application toward a more secure data-handling architecture.
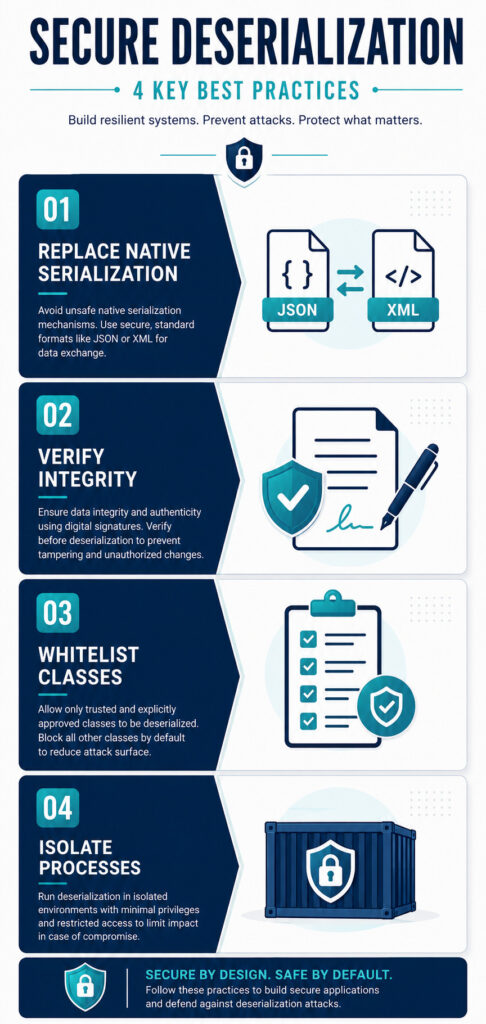
| Strategy | Action | Priority |
| Data Formats | Replace native serialization with JSON or XML | High |
| Integrity | Use digital signatures or HMACs on data | High |
| Whitelisting | Limit class instantiation to safe types | Medium |
| Isolation | Run processes in low-privilege containers | Medium |
To secure your application, focus on these defensive strategies. Whenever possible, migrate away from native serialization libraries to safe, platform-agnostic formats.
These formats are much harder to manipulate into executable code. Always verify the integrity of the data stream using digital signatures or HMACs to ensure the data has not been tampered with in transit.
How to Approach Proactive Threat Modeling for Serialization?
Proactive threat modeling helps you identify deserialization risks before a single line of code is written. Instead of patching flaws after a scan, you map out your data flow early.
“Deserialization vulnerabilities often remain hidden in the deep logic of the application, making them difficult to detect with automated scanners alone.” – Web Security Academy
Identify every interface where data crosses from an untrusted source to your application memory. Evaluate whether you truly need to use native serialization or if a flat data format suffices.
Review your third-party dependencies specifically for known gadgets. Create a deny-list or allow-list architecture early in the design phase, ensuring that only expected object classes are permitted.
This design-first approach shifts security to the left. It reduces the likelihood of a major deserialization flaw reaching production.
Can Automated Scanners Detect All Deserialization Flaws?
No. While automated tools can detect obvious flaws, they often fail to identify custom gadget chains or business-specific logic vulnerabilities.
Manual review remains a critical part of your testing process. Scanners typically look for standard, known signatures. Deserialization vulnerabilities rely on complex gadget chains specific to your application’s classpath.
These are difficult for scanners to model without deep context. It is never safe to deserialize untrusted user input directly.
You should always treat incoming serialized data as malicious and validate it rigorously before processing it in memory. If you cannot update your dependencies, you must apply compensating controls.
FAQ
Are certain development environments more susceptible to these vulnerabilities?
Deserialization flaws are not limited to any specific language or framework. While they were historically associated with Java, modern web applications built on PHP, Python, Ruby, and .NET frequently encounter these issues when processing serialized data.
Can a Web Application Firewall provide full protection against these attacks?
Web Application Firewalls offer limited efficacy against deserialization attacks. They are designed to catch known patterns, but they often fail to identify complex, custom gadget chains that are unique to your application’s classpath.
What mitigation steps are necessary if I cannot immediately update a vulnerable library?
If immediate updates are not feasible, you must implement compensating controls. This includes running the deserialization process in a highly restricted, low-privilege sandbox and applying strict class whitelisting to prevent unintended object instantiation.
Is the deserialization of JSON objects inherently safer than binary formats?
JSON is generally safer than native binary serialization, but it is not immune to risk. If your parser is configured to instantiate complex objects or execute logic during the parsing phase, it remains vulnerable to object injection and manipulation.
What is the recommended frequency for auditing serialization logic?
You should treat serialization logic as a high-risk attack surface. Audit these components during every major library update, whenever the object structure changes, or during scheduled quarterly security assessments.
Strengthening Trust Through Data Integrity
Using integrity checks deserialization is an effective way to protect applications from tampered or malicious serialized data before it is processed.
By validating data integrity, verifying trusted sources, and combining integrity checks with secure deserialization practices, organizations can reduce the risk of unauthorized object manipulation and other deserialization-based attacks.
Making these controls a standard part of your application security strategy helps ensure that only trusted data is accepted throughout the software lifecycle.
Ready to strengthen your secure development and security practices? Join the Secure Coding Practices Bootcamp and learn practical, hands-on techniques for validating application data, preventing insecure deserialization vulnerabilities, and building resilient software from day one.
References
- https://cwe.mitre.org/data/definitions/502.html
- https://portswigger.net/web-security/deserialization